Microsoft CEO Nadella Warns AI-Driven Patching Increases Outage Risks
Microsoft CEO Satya Nadella warned that AI tools identifying software vulnerabilities faster than companies can test fixes are increasing global outage risks. Citing a recent Microsoft service disruption and industry-wide instability, Nadella explained that critical patches must be deployed instantly to counter active exploitation, often bypassing safety testing protocols.
Key points
- Satya Nadella, the CEO of Microsoft, stated that AI tools are discovering software flaws faster than organizations can safely test and implement fixes.
- Nadella acknowledged that a recent global Microsoft outage was caused by a latent bug invoked by a patch, admitting the company should have conducted more thorough testing.
- He explained that because attackers exploit newly discovered vulnerabilities immediately, critical security patches must move directly from availability to production without standard testing windows.
- The rapid deployment of untested patches is cited by banks and the NSA as a contributing factor to recent widespread US service disruptions.
- Nadella noted that the baseline level of cyberattacks has increased, as AI lowers the barrier for attackers to identify and exploit software weaknesses.
The Speed of Vulnerability Discovery
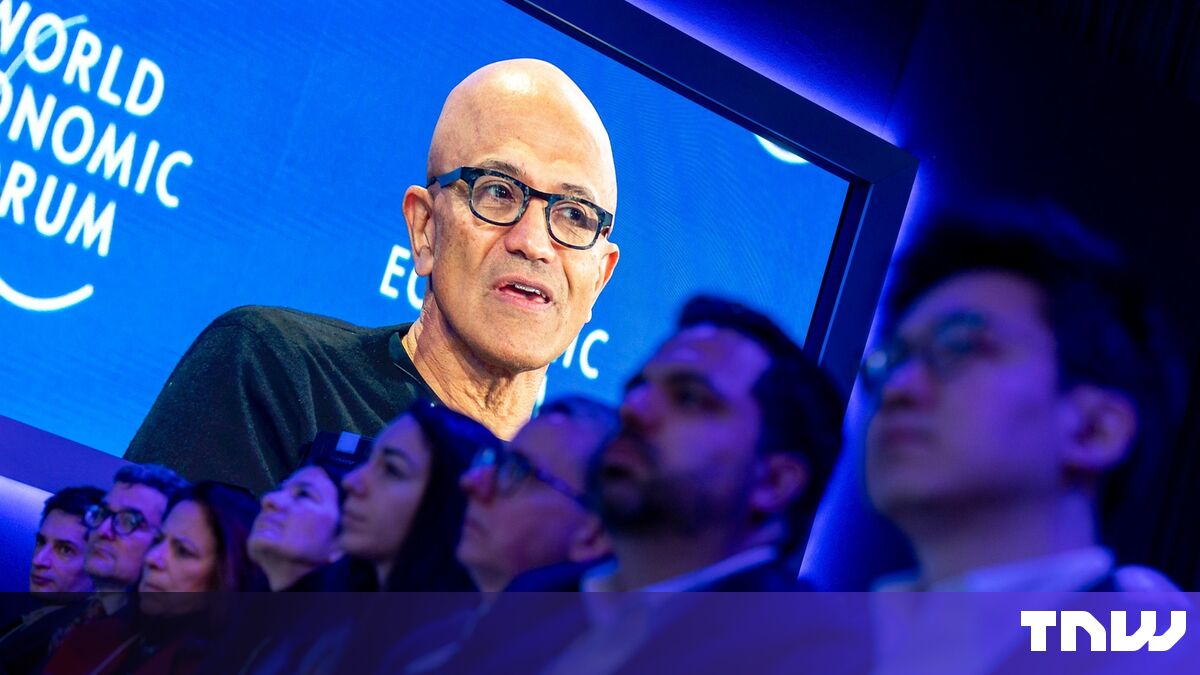
Satya Nadella, chief executive of Microsoft, issued a stark warning regarding the intersection of artificial intelligence and software stability during a panel at The New York Times’ DealBook Summit in New York on Wednesday. Nadella argued that the integration of AI into security workflows is fundamentally altering the risk landscape for global technology infrastructure. He stated that AI tools are now capable of identifying software flaws at a pace that outstrips the ability of engineering teams to verify and safely deploy corrections. This acceleration creates a structural vulnerability where the speed of discovery exceeds the speed of validation, leading to increased instability in critical systems.
Recent Service Disruptions
The comments followed a significant outage affecting Microsoft Outlook and other services earlier in the week. Nadella addressed the incident directly, clarifying that the disruption was not caused by AI tools but was instead the result of a latent bug within Microsoft’s own codebase. He described the event as a "perfect storm" where the bug was invoked by a specific action. In a subsequent interview with CNBC’s Jim Cramer, Nadella conceded that Microsoft could have done more to prevent the global outage. He admitted that the company should have implemented more rigorous testing protocols and established better system "bulkheads" to contain the failure and prevent it from cascading across global networks.
The Patching Dilemma
A central theme of Nadella’s address was the operational pressure placed on software developers by the current threat environment. He contrasted the current reality with previous standards, noting that a fix for a critical banking system typically received a week of testing in the past. Today, that window has effectively vanished. Nadella explained that because attackers are exploiting newly surfaced flaws immediately, security patches must move instantaneously from availability to production deployment. This necessity forces organizations to bypass traditional safety checks, introducing a higher probability of instability. On the day of his remarks, Nadella highlighted that three critical patches had landed for open-source packages, illustrating the relentless pace at which vulnerabilities are addressed in the wild.
Industry and Government Response
The phenomenon of rushed patching has drawn attention from major financial institutions and government agencies. Reports indicate that banks and the National Security Agency (NSA) have linked recent widespread US outages to the deployment of hastily applied patches for AI-discovered flaws. This attribution underscores a growing consensus among regulators and industry leaders that the current model of automated vulnerability detection and immediate remediation is creating systemic fragility. The reliance on speed over verification is resulting in collateral damage to essential services, prompting calls for a reevaluation of how security updates are managed in highly interconnected digital ecosystems.
The Rising Baseline of Threats
Beyond the mechanics of patching, Nadella emphasized a broader shift in the cyber threat landscape. He stated that the "floor of cyberattacks has fallen," meaning that the baseline volume and ease of conducting attacks have increased significantly. With the advent of advanced AI models, individuals with limited technical expertise can now identify and exploit software weaknesses that previously required specialized knowledge. This democratization of attack capabilities means that defenders are facing a larger number of threats from a wider array of actors. The combination of easier exploitation and faster, less tested fixes creates a volatile environment where outages are likely to become more frequent as AI continues to accelerate both the discovery of bugs and the methods used to exploit them.
Sources
The WireByte editorial team synthesises technology news from multiple primary sources, verifies the facts, and links every source. Articles are produced with AI assistance and reviewed under our editorial policy.