Apple to Scan iCloud Public Links for Harmful Content in iOS 27.3
Apple will scan iCloud files shared via public links for harmful content starting with iOS 27.3. This change removes end-to-end encryption for shared items and allows Apple to delete content or block accounts. The move follows activist pressure to combat child abuse material, though the definition of 'harmful' remains undefined.
Key points
- Apple Inc., the technology giant, will implement content scanning for iCloud public links starting with the iOS 27.3 update.
- The update, expected in December, applies to iOS, iPadOS, macOS, and visionOS, affecting files shared via the 'Anyone with the link' option.
- Sharing content publicly will remove end-to-end encryption, making files accessible to Apple for scanning purposes.
- Apple reserves the right to modify, remove, or delete flagged content and may block user accounts or involve law enforcement.
- The policy follows activist campaigns targeting child sexual abuse material, though Apple has not defined 'harmful content' in its documentation.
Encryption Changes for Public Sharing
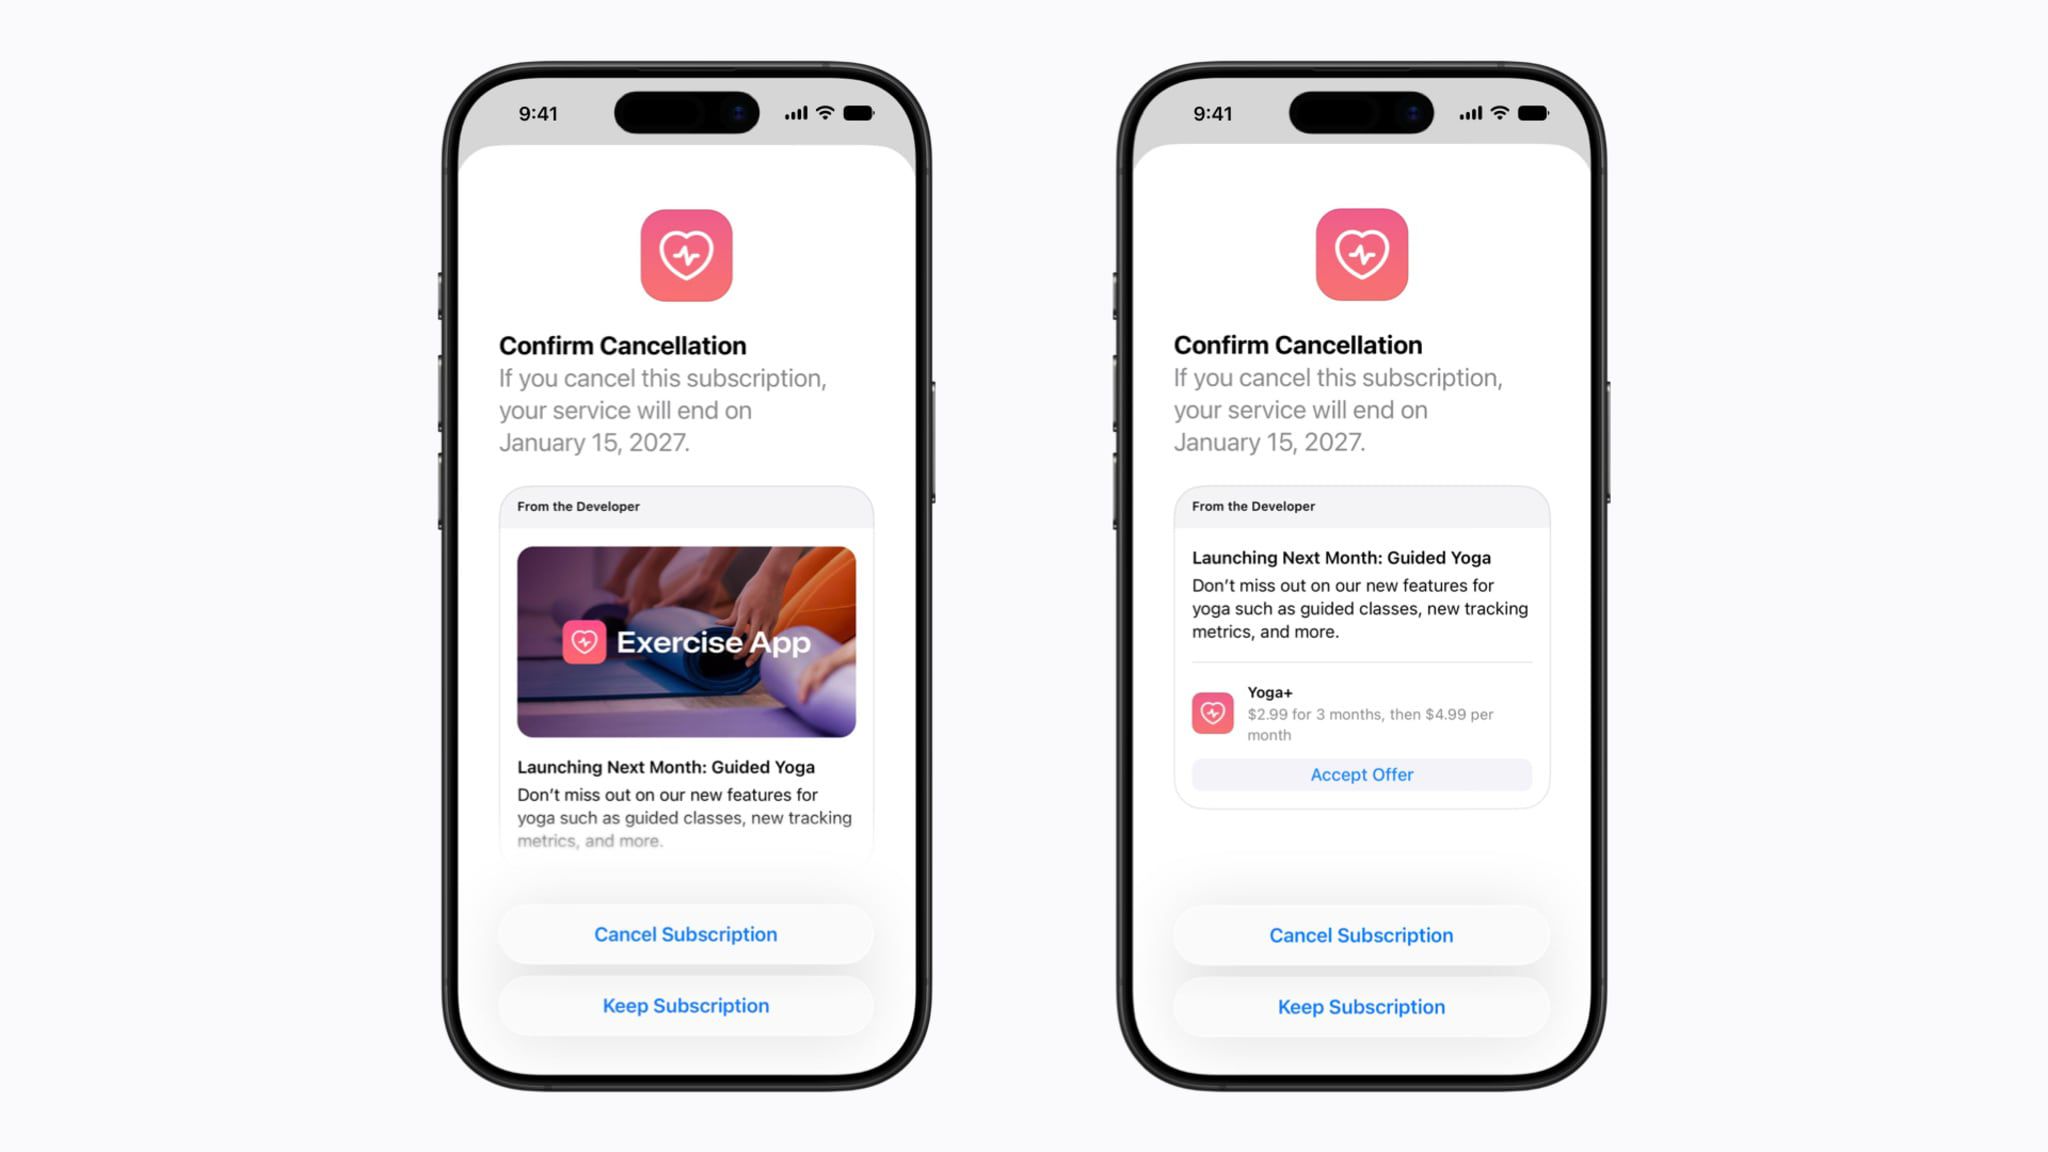
Apple is introducing a significant modification to its iCloud privacy framework with the upcoming iOS 27.3 update. According to a newly published support document, the company will begin checking content shared via public iCloud links for harmful material. This change affects the 'Anyone with the link' sharing option, which allows users to distribute photos, files, and other items stored in iCloud Photos or iCloud Drive to any recipient possessing the URL. Previously, such shared items maintained end-to-end encryption, ensuring that only the sender and recipient could access the data. Under the new protocol, sharing via public link will no longer be end-to-end encrypted, rendering the content accessible to Apple for automated scanning.
Scope of the Update
The policy shift is not limited to mobile devices. The support document confirms that the scanning mechanism will be implemented across iOS 27.3, iPadOS 27.3, macOS 27.3, and visionOS 27.3. Apple released the first developer betas for these operating systems recently, signaling that the final public release is targeted for December. The company states that when users choose to share an item using the public link method in version 27.3 or later, that content is explicitly made accessible to Apple to facilitate the check for harmful content. This represents a structural change to how iCloud handles data privacy for shared files, distinguishing them from private storage which remains encrypted.
Enforcement and Consequences
Apple has outlined specific consequences for content that triggers its harmful content filters. The support document indicates that the company reserves the right to move, refuse, modify, remove, or delete any content identified as harmful. Beyond content removal, Apple may take punitive actions against user accounts. These measures include blocking or disabling existing accounts, preventing users from creating new accounts, and, if necessary, invoking law enforcement. The document does not specify the exact thresholds or algorithms used to determine what constitutes harmful content, leaving the definition open to interpretation by the company.
Context and Activist Pressure
This policy change follows years of pressure from activists and advocacy groups urging tech companies to crack down on child sexual abuse material (CSAM) stored on their platforms. The term 'harmful content' is widely understood in this context to include CSAM, although Apple has not explicitly defined the scope in its public documentation. The move aligns with broader industry trends where privacy protections are being weighed against safety concerns raised by civil society. Critics of such scanning mechanisms often argue that breaking end-to-end encryption creates vulnerabilities that could be exploited by malicious actors, while proponents argue it is necessary to protect vulnerable populations.
Key takeaways
- Apple will scan iCloud files shared via public links for harmful content starting with iOS 27.3.
- The update removes end-to-end encryption for files shared using the 'Anyone with the link' option.
- Apple can delete content, block accounts, or involve law enforcement based on the scan results.
- The change applies to iOS, iPadOS, macOS, and visionOS, with a public release expected in December.
- The policy follows activist pressure to combat child sexual abuse material, though 'harmful content' is not defined.
Sources
The WireByte editorial team synthesises technology news from multiple primary sources, verifies the facts, and links every source. Articles are produced with AI assistance and reviewed under our editorial policy.